Protecting Against Modern Phishing
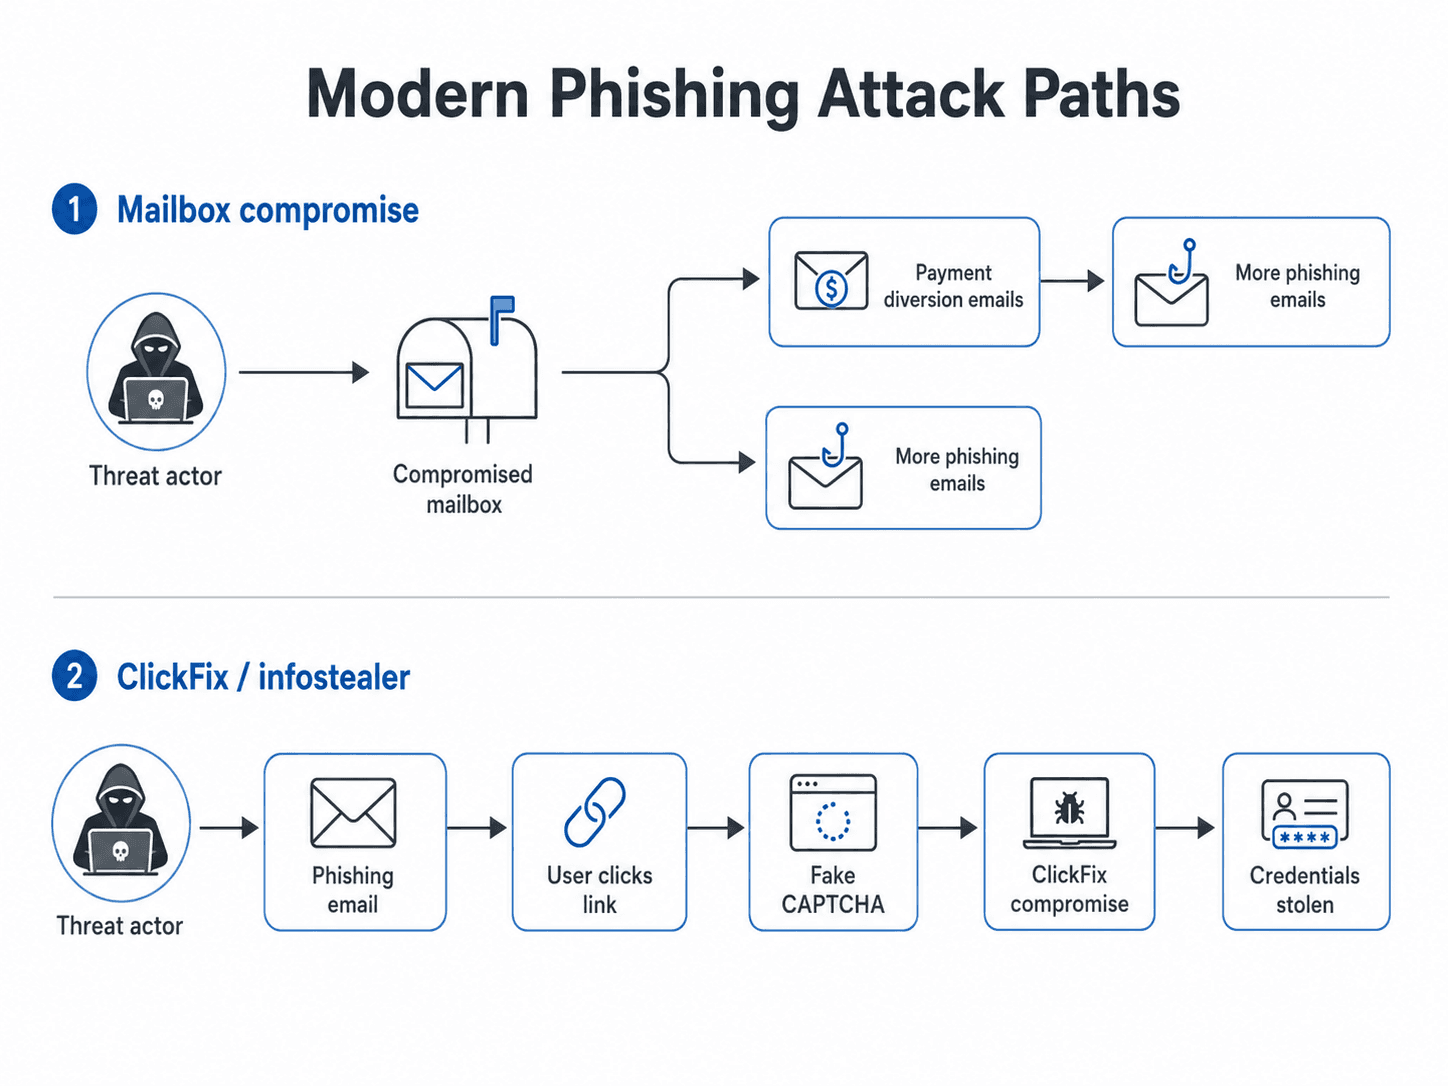
Modern phishing no longer always looks fake. This guide explains how mailbox-led attacks, SharePoint lures, device code phishing and ClickFix pages work, and what organisations should train, block and monitor.
Threat Intelligence
Incident response is a goldmine for up-to-date threat actor tactics and techniques. Read about what we're seeing, and how businesses can protect themselves.
Latest research
Loading threat intelligence articles…

Two critical PHP flaws expose web servers to remote code execution. Jordan Newman examines exploitation conditions, forensic limitations, and a Sigma detection rule.

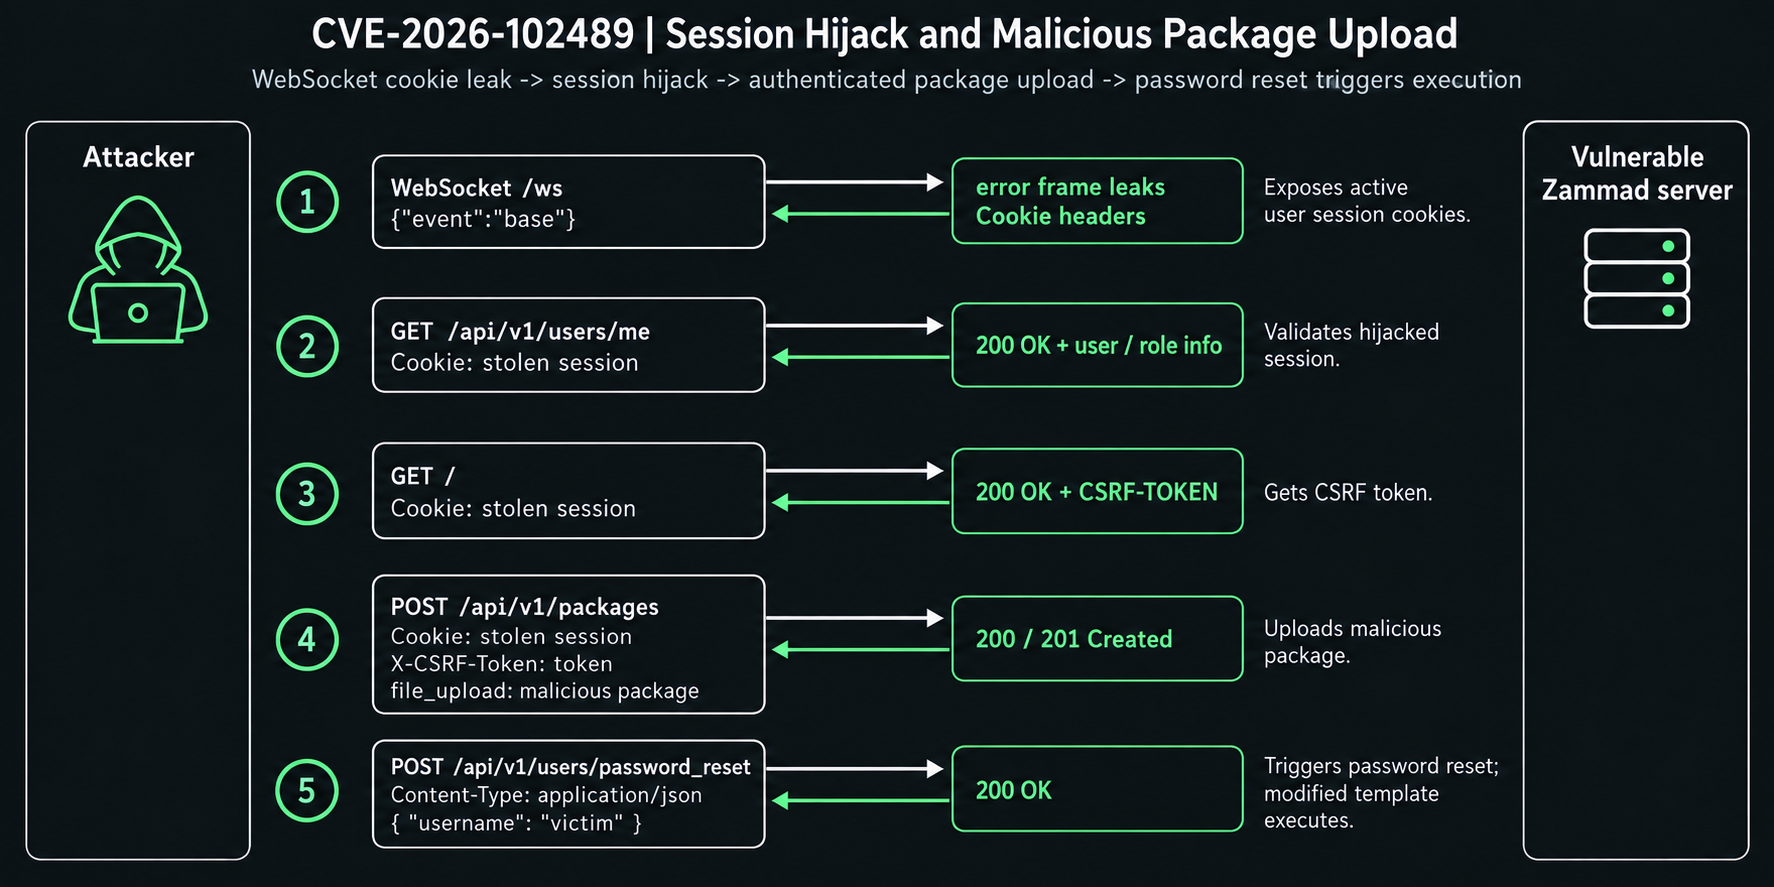
We examine the Zammad exploit chain used against DIVD, reproduce initial access in our lab, and show how Strand reconstructs the attack from forensic evidence.

Threat actors are moving from VPNs to residential proxies, routing attacks through ordinary home connections. How they work, and how Strand now detects them.